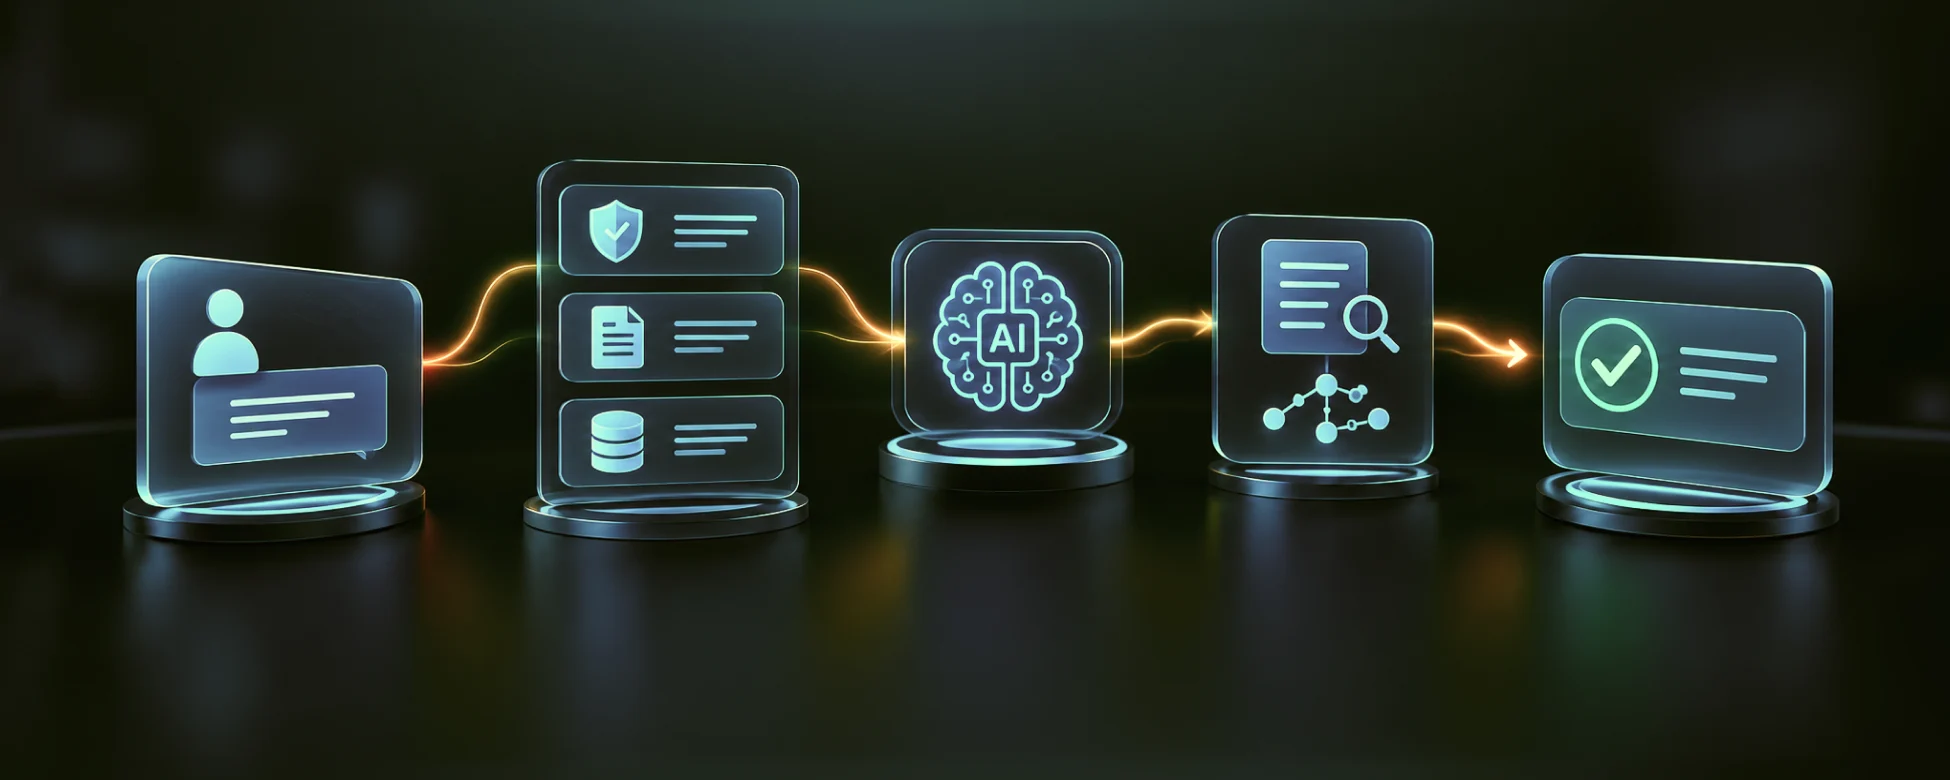

An AI audit trail is a record showing what happened during an AI interaction, the decision made, the policies evaluated, the data involved, the timestamp, and the reasoning path that led to the outcome. It exists so that an organization can reconstruct, after the fact, exactly why an AI interaction was allowed, adjusted, or blocked, rather than relying on memory, application logs, or guesswork.
Why It Matters
When a regulator, auditor, or internal risk committee asks an organization to prove that an AI policy was actually enforced on a specific date, "we believe so" isn't an acceptable answer. Most organizations discover this gap the hard way, during an audit, after an incident, or when a client demands evidence of data handling, only to find that their AI interactions left no reconstructable trail at all. Application logs weren't designed for this; they capture technical execution, not the governance reasoning behind a decision. An audit trail purpose-built for AI activity closes that gap by design, capturing the decision itself alongside the evidence that produced it.
How It Relates to AI Governance
An audit trail is the evidentiary output of a governance layer's evaluation process; every governed interaction should produce one automatically, without requiring manual reconstruction later. It typically separates governance evidence (what was decided and why) from AI execution data (which model was used, latency, cost), while keeping both linked to the same interaction, so compliance and engineering teams can each get the view relevant to them.