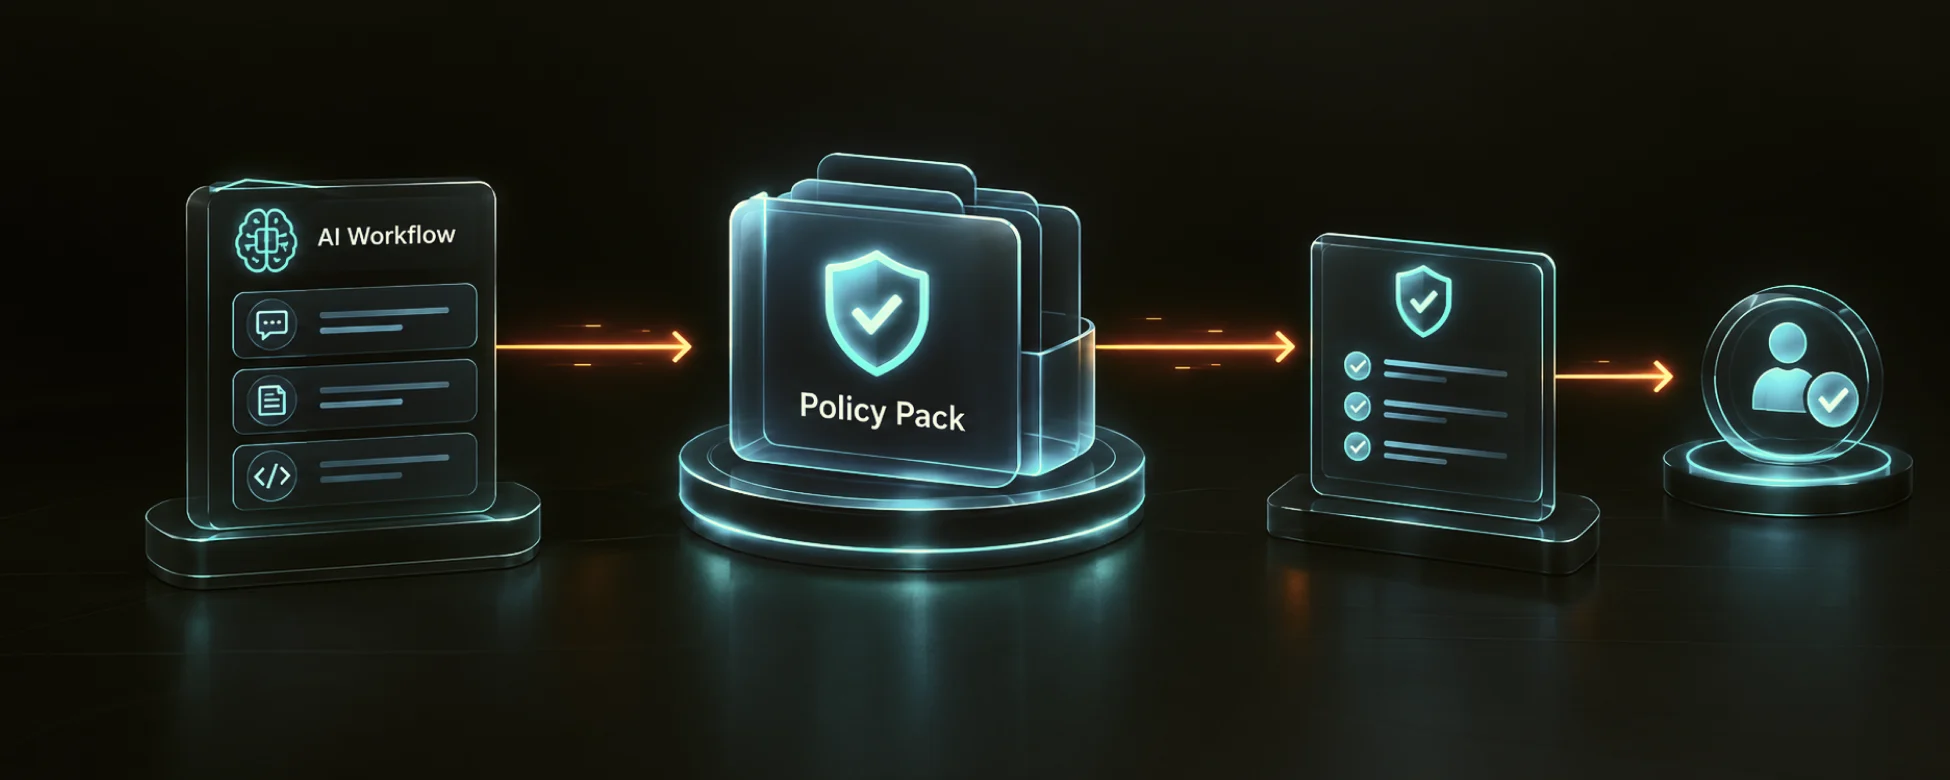

A Policy Pack is a reusable, bundled set of governance rules, regulatory, industry-specific, or organization-specific, applied to an AI workflow to evaluate whether an interaction complies with defined requirements. Instead of writing bespoke rules per application, a Policy Pack lets an organization apply a consistent, pre-built set of controls, such as GDPR data-privacy rules or FINRA suitability requirements, across every workflow where that risk applies.
Why It Matters
AI risk isn't uniform; a wealth-management chatbot and an internal HR copilot face entirely different regulatory exposure, yet many organizations apply the same generic guardrails to both, or none at all, because building risk-specific controls per application is slow and rarely prioritized until something goes wrong. A Policy Pack model separates rule logic from the application: the same GDPR pack can apply to five different workflows without five separate implementations, and multiple packs can stack on one workflow when more than one risk category applies. A financial advisory tool might run a general privacy pack alongside a suitability-specific one simultaneously.
How It Relates to AI Governance
Policy Packs are what make a governance layer practically scalable. Instead of hand-coding every regulatory or business rule into every application, packs let governance and compliance teams define a rule once, sometimes drafted from an existing policy document and translated into technical conditions, with human review before activation, and apply it wherever that risk exists. This turns policy from something interpreted ad hoc by developers into a controlled, reusable asset.