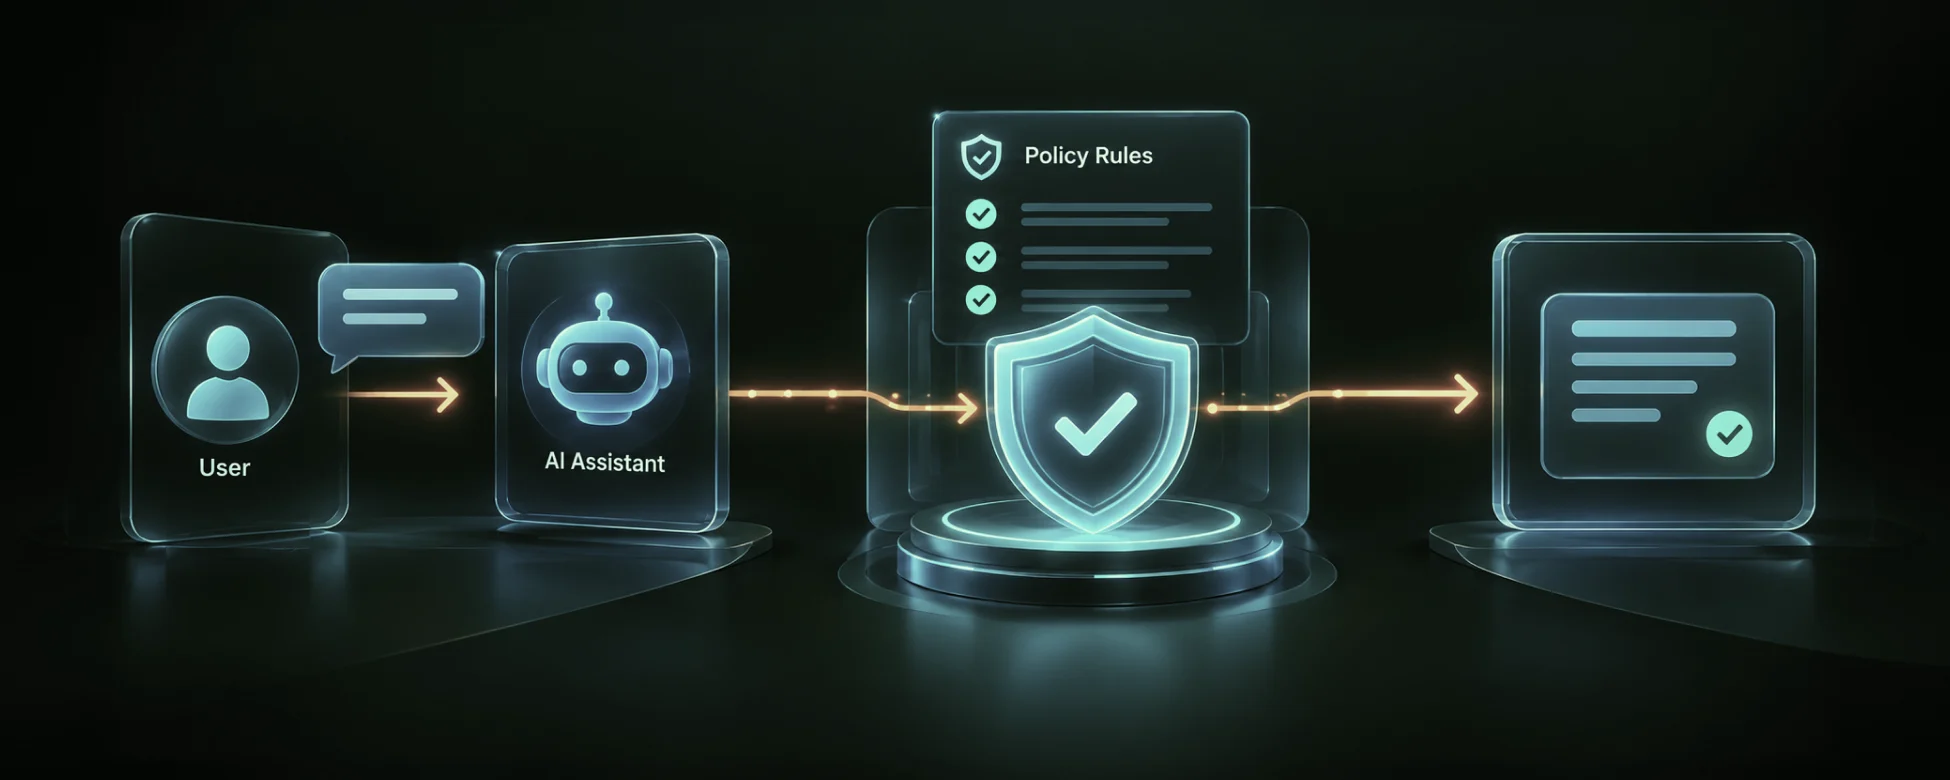

Runtime policy enforcement is the practice of evaluating an AI interaction against governance rules while it is happening, rather than reviewing it after the fact. Instead of discovering a policy violation days later in a log review, the system checks the input, output, or document in real time and returns a decision before the activity is allowed to proceed.
Why It Matters
The conventional compliance model , write a policy, hope it's followed, review logs periodically to catch violations, breaks down with AI because the pace and volume of interactions make after-the-fact review impractical. By the time a compliance team notices that an employee shared confidential client data with a chatbot, that data has already left the organization's control; the review only confirms a loss occurred. Runtime enforcement changes the sequence: the check happens before the AI model receives the content, so the loss can be prevented rather than merely documented. This proportional response matters too; not every issue needs the same treatment; some interactions should be blocked outright, others adjusted or sanitized before continuing.
How It Relates to AI Governance
Runtime enforcement is what separates an active governance layer from a passive monitoring tool. Monitoring tells you what happened; enforcement determines what happens next, in the moment, based on policy rules evaluated against the actual content of the interaction. It's the mechanism that turns a written policy into a technical control embedded directly in the execution path of an AI workflow.